The arrest of fifteen individuals inside a Mandaluyong City condominium in May 2026 did not look, at first, like a breakthrough in the fight against cybercrime. It looked like a routine raid. But the digital forensic examination that followed exposed something more troubling than a single fraudulent website: a coordinated scamming network that had industrialized the art of imitation, using a spoofed cryptocurrency platform to solicit investments from victims who believed they were dealing with a legitimate exchange .
The Anatomy of a Spoofed Crypto Website
Spoofed websites are not new. What distinguishes the Mandaluyong operation is the level of operational discipline behind it. According to the National Bureau of Investigation, the group—allegedly led by an individual identified only as “Boss Choi”—used a fraudulent website designed to mimic legitimate cryptocurrency trading platforms . Victims were solicited to invest, and the site presented the familiar interface of a functioning exchange: account dashboards, portfolio trackers, deposit prompts. The illusion held long enough for funds to be transferred.
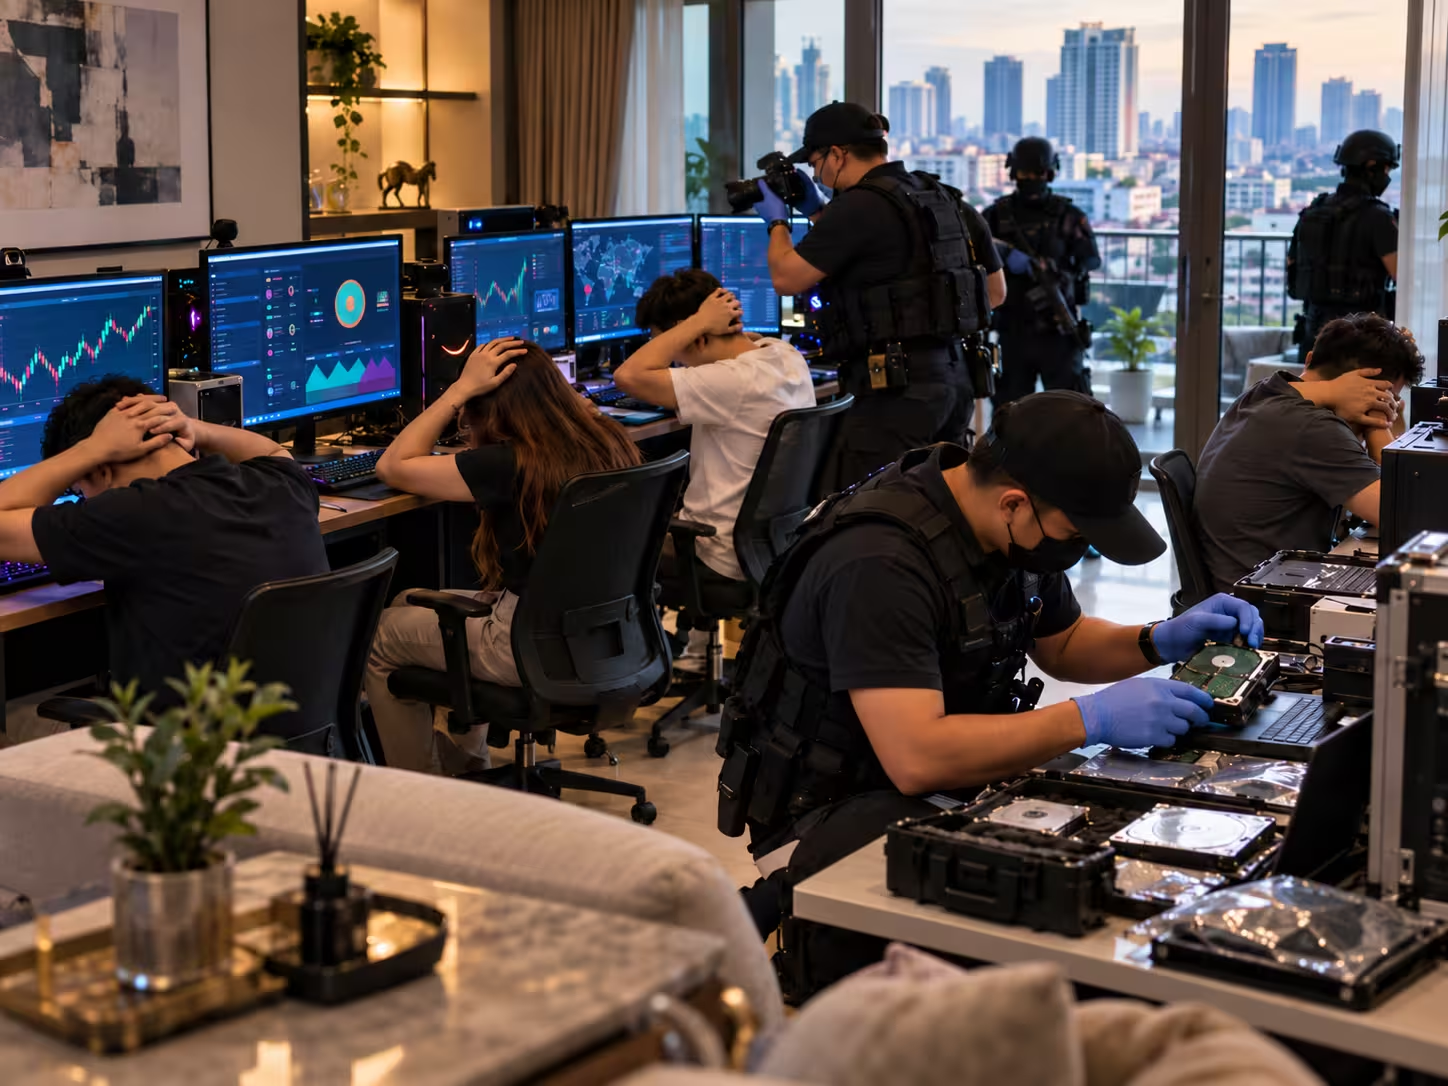
The NBI’s Dangerous Drugs Division and Digital Forensic Laboratory Division executed a Warrant to Search, Seize, and Examine Computer Data at the condominium on May 9, 2026, supported by the Philippine Air Force Intelligence Unit . Fifteen suspects were caught working on desktop computers at the time of the raid: one Chinese national, one Malaysian national, twelve Filipino males, and one Filipino female . The on-site forensic examination revealed critical digital data that served as tools for computer-related forgery under Republic Act No. 10175, the Cybercrime Prevention Act of 2012 .
From POGO Collapse to Scam Hub: The Bigger Picture
The case cannot be understood in isolation. NBI Director Melvin Matibag framed the operation as part of a broader enforcement posture against financial scams in cyberspace, noting that the individuals involved were linked to former Philippine Offshore Gaming Operator (POGO) operations that had collapsed into scam hubs . This is the critical context: the infrastructure, personnel, and technical know-how of defunct gaming operations did not disappear. They migrated into cryptocurrency fraud, where spoofed websites became the new storefront.
The legal consequences arrived swiftly. Thirteen of the accused pleaded guilty to the lesser offense of Aiding or Abetting in the Commission of Cybercrime and were sentenced to three years of imprisonment by the Mandaluyong City Regional Trial Court Branch 211 on May 26, 2026 . The convictions signal that Philippine courts are willing to treat spoofed-platform fraud not as a technical misdemeanor but as a serious cybercrime with carceral consequences.
Forensic Evidence and the Forgery Pipeline
What makes the Mandaluyong case instructive for investors and regulators alike is the forensic clarity of the operation. The seized devices contained digital data used as instruments for computer-related forgery—meaning the spoofed website was not a crude phishing page but a maintained digital asset with infrastructure behind it . The NBI described the evidence as indicating an organized scamming network, not a handful of opportunistic fraudsters .
For investors, the lesson is uncomfortable: a professional-looking crypto platform can be fabricated, maintained, and operated by a team working from a residential condominium. The presence of foreign nationals alongside Filipino operatives suggests a transnational dimension that complicates enforcement and victim recovery.
Why This Case Matters Beyond the Philippines
The Mandaluyong crackdown is a data point in a larger trend. The Philippine Securities and Exchange Commission has separately warned against unregistered crypto trading platforms, reminding the public that platforms operating without authorization fall outside the regulatory perimeter . When spoofed sites imitate legitimate exchanges, the regulatory warning becomes even harder to apply: victims cannot distinguish between an unregistered platform and a counterfeit one.
The NBI’s operation demonstrates that enforcement can move quickly when forensic evidence is preserved at the point of arrest. But it also reveals the asymmetry: a spoofed website can be stood up in days, while investigations, warrants, and prosecutions take months. The three-year sentences secured in May 2026 are a deterrent signal, but the infrastructure of imitation remains cheap and replicable.